Library / Blogs
SurveyMonkey Engineering Blog
Easily create surveys and forms with AI and templates for employee and customer feedback, market research, event registrations and more. Get started free.
By SurveyMonkey engineers · SurveyMonkey · Added 2026-10-12
All content belongs to SurveyMonkey engineers / SurveyMonkey. We only link to it and give credit. Report a problem
Learn this article
About 37 min left. Your work is saved as you go.
What you are about to study
SurveyMonkey wrote this to explain how they thought about a problem. You should know the basics: caching, queues and replication.
Ideas you will meet
- Distributed Systems
- Consensus, time, failure and the fundamentals of scale-out.
What we already know about this
Our own lessons on these ideas. Read them here before you start, so it makes sense.
Core Concepts: How Things Actually Work · 8 minHow HTTPS worksCertificates, key exchange and encryption in plain language: what the padlock actually proves.Read here
What it provides
HTTPS is HTTP inside TLS. TLS gives three things:
- Confidentiality: outsiders cannot read the traffic.
- Integrity: tampering is detected.
- Authentication: you are talking to the real owner of the domain.
The handshake, simplified
100%Figure SDA-CORE-05-1 · The handshake, simplified · © forcsguy.com
- The browser says which versions and ciphers it supports.
- The server answers with a certificate containing its public key.
- The browser checks the certificate: signed by a trusted authority, matches the domain, not expired, not revoked.
- They run a key exchange (modern TLS uses ephemeral Diffie-Hellman) to agree on a secret that never crosses the network.
- From that secret both sides derive symmetric session keys and encrypt everything after.
TLS 1.3 shortens this to one round trip, and can resume with none.
100%Figure SDA-CORE-05-2 · The order of a secure page load · © forcsguy.com
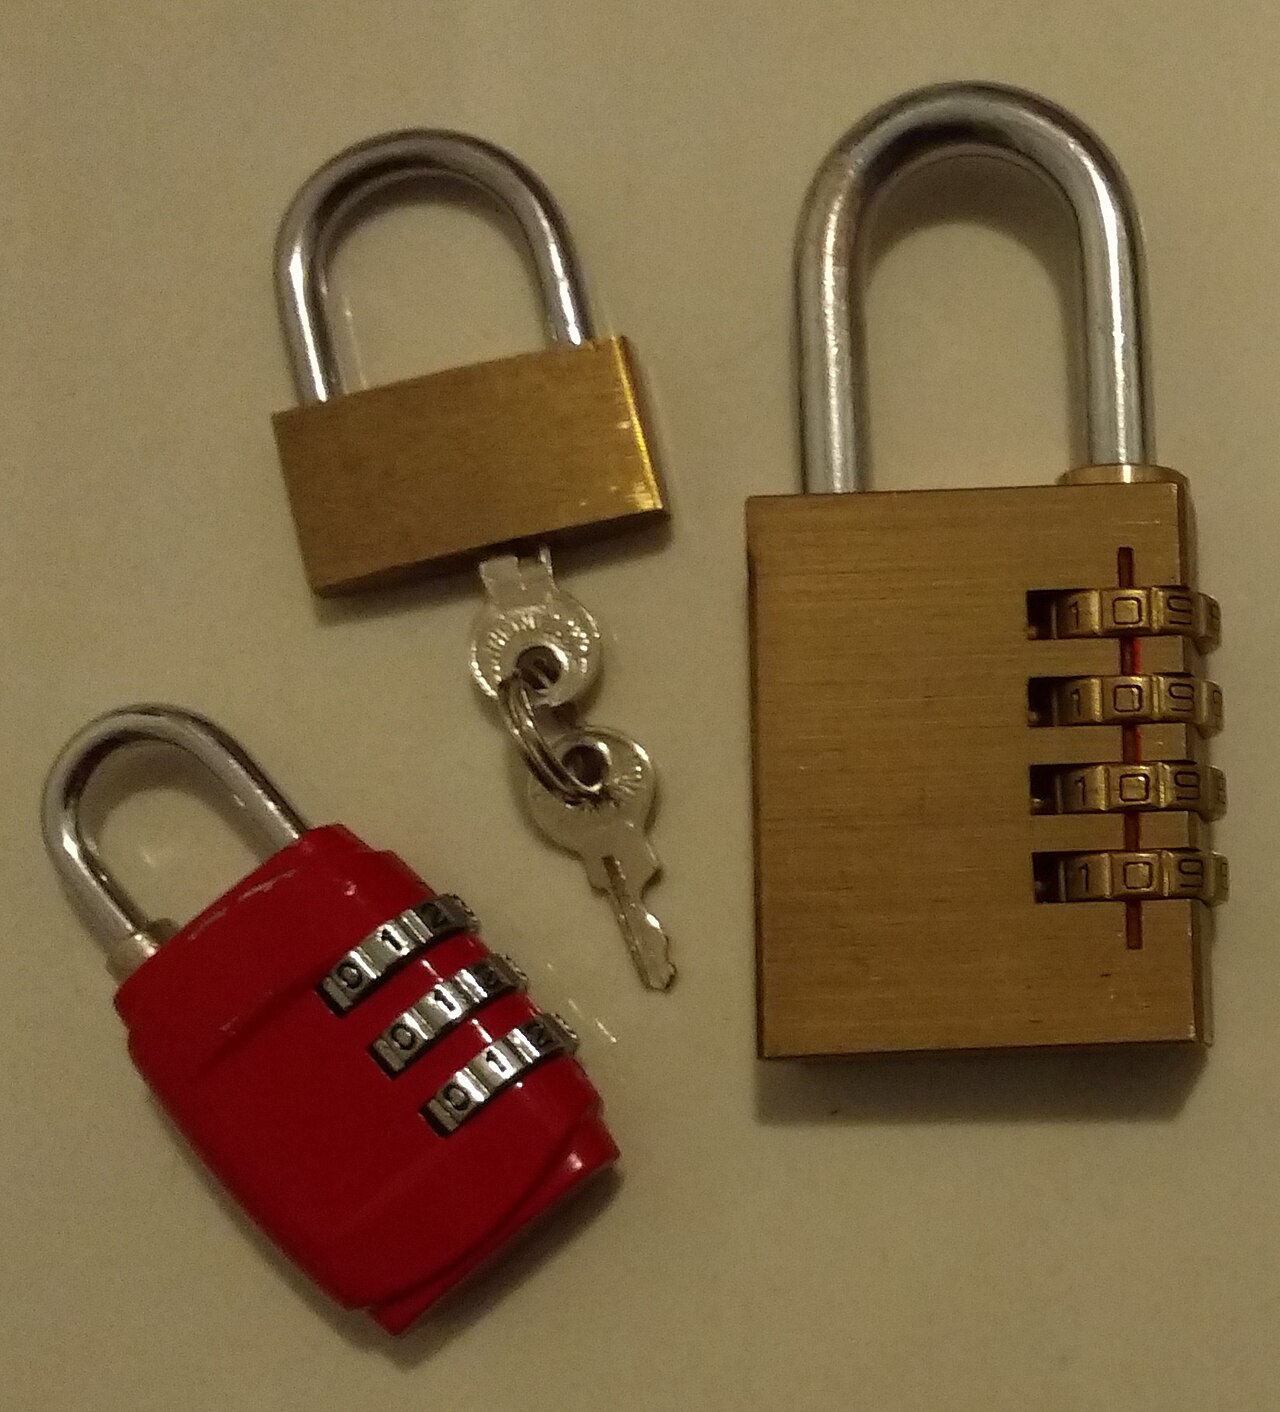 Image: Mx. Granger · CC0 · Source · Wikimedia Commons: Three padlocks
Certificates and trust
A certificate says "this public key belongs to example.com", signed by a certificate authority. Your browser and operating system ship with a list of trusted CAs. A server presents a chain (its certificate, plus intermediates) that leads to one of them.
Free automated certificates (for example from Let's Encrypt) made HTTPS the default. Certificates expire, so renew automatically and monitor expiry: an expired certificate is a common cause of outages.
A useful detail: asymmetric operations are one-way in practice. Anyone can encrypt or verify with the public key, but only the private-key holder can decrypt or sign. That asymmetry is what lets strangers agree on a secret over an open network, and why the session then switches to a much faster shared symmetric key.
Forward secrecy
With ephemeral key exchange, each session uses fresh keys. If the server's long-term key is stolen later, old recorded traffic still cannot be decrypted.
What HTTPS does not do
- It does not make a site trustworthy: phishing sites use HTTPS too.
- It does not hide which site you visit from the network (the domain is visible in DNS and sometimes in the handshake).
- It does not protect data once it reaches the server: you still need good storage security.
Practical checklist
- Redirect HTTP to HTTPS and send an HSTS header so browsers refuse plain HTTP.
- Use TLS 1.2 or 1.3 only; disable old protocols.
- Mark cookies
SecureandHttpOnly. - Automate certificate renewal and alert before expiry.
Real-world reading
Related reading
- Chrome Developers BlogGoogle engineers · GoogleBlogs
- RFC 9000: QUICIETFDocumentation
- Web VitalsGoogle web.dev · GoogleDocumentation
- Domain-Driven Design ReferenceEric Evans · Domain LanguageBooks
Show 6 moreShow fewer
- Traffic Infrastructure (Edge Network) at DropboxDropbox engineers · DropboxCase Studies
- .NET Engineering Blog.NET engineers · .NETBlogs
- Anthropic BlogAnthropic engineers · AnthropicBlogs
- OLX Engineering BlogOLX engineers · OLXBlogs
- monday.com Blogmonday.com engineers · monday.comBlogs
- SurveyMonkey Engineering BlogSurveyMonkey engineers · SurveyMonkeyBlogs
Go deeper on this
A path through videos, articles, other case studies and code on the same ideas as SurveyMonkey Engineering Blog.
Warm upGet the vocabulary first.
Books · Free from the author
Concurrent and Distributed Systems (Cambridge lecture notes)
Eight lectures on time, broadcast, replication, consensus and transactions, with notes, slides and video. Free from the author under CC BY-SA.
University of CambridgeIntermediate
Books · Free from the author
Computer Networks: A Systems Approach
How networks are built and why: protocols, routing, congestion control and the internet's architecture. The authors publish it free online under CC BY 4.0.
Systems ApproachIntermediate
WatchHow others solve the same problem, on video.
Videos belong to their creators and play from YouTube. More on YouTube (opens in a new tab)
ReadEngineers explain it in their own words.
Blogs · Free from the author · Read here
Scalable Web Architecture and Distributed Systems
A full chapter on the building blocks of large websites: availability, performance, reliability, scalability, caches, proxies, indexes, load balancers and queues. Free to read here under CC BY 3.0.
The Architecture of Open Source ApplicationsBeginner40 min
Papers · Read here
Facebook’s photo storage
This paper describes Haystack, an object storage system optimized for Facebook’s Photos application. Facebook currently stores over 260 billion images, which translates to over 20 petabytes of data.
USENIXIntermediate
See it in another companyThe same ideas, a different system.
Case Studies · Read here
Aroma: Using ML for Code Recommendation at Facebook
Thousands of engineers write the code to create our apps, which serve billions of people worldwide. This is no trivial task—our services have grown so diverse and complex that the codebase contains…
FacebookIntermediate
Case Studies · Read here
Brooklin: Distributed Service for Near Real-Time Data Streaming at LinkedIn
Brooklin—a distributed service for streaming data in near real-time and at scale—has been running in production at LinkedIn since 2016, powering thousands of data streams and over 2 trillion messages per day. Today, w...
LinkedInIntermediate
Read the codeSee how it looks when it is real.
GitHub
Engineering Blogs
A huge directory of company engineering blogs to learn from real production systems.
kilimchoiIntermediate
GitHub
Awesome Scalability
Curated reading list of articles on the architecture of scalable, reliable systems.
binhnguyennusIntermediate
Keep learning
Loading community…